Single sign-on
Learn how to set up single sign-on
Bunny supports single sign-on via SAML to enable a more secure and frictionless login experience.
Bunny also supports SCIM for automated user provisioning. Follow this SAML setup and then head over and setup SCIM.
Step 1 - Configure the identity provider Link to Step 1 - Configure the identity provider section
Login to your identity provider and add a new SAML application.
- On the Applications tab click to Add a new application.
- Search for “SCIM Provisioner w/SAML (SCIM v2 w/OAuth & Scope)” and select the application with this name.
- Change the app name to Bunny and then click save.
-
On the Configuration tab enter the following values (substituting your Bunny subdomain) and click Save.
SAML Audience URL
https://{{subdomain}}.bunny.com/api/authorizations/saml/metadata
SAML Consumer URL
https://{{subdomain}}.bunny.com/api/authorizations/saml
Site
https://{{subdomain}}.bunny.com - Assign the app to your test user account.
Ignore the SCIM related fields for now. We’re only setting up SAML here and will configure the SCIM fields later.
- In the Admin section under Applications click to Create a new App integration.
- The type of integration is SAML 2.0
- Give the app a name “Bunny”
- Set the following fields
Single sign-on URL
https://{{subdomain}}.bunny.com/api/authorizations/saml
Audience URI (SP Entity ID)
https://{{subdomain}}.bunny.com/api/authorizations/saml/metadata - Set the Name ID format to EmailAddress
- Set the Application username to Email
- Click to save the application then scroll down to the SAML Signing Certificates section and click the button to View SAML setup instructions.
- Keep the instructions open, you will need them in the next step.
Step 2 - Configure BunnyLink to Step 2 - Configure Bunny section
The next step is to copy the SAML fields from the identity provider and paste them back into Bunny.
Log in to your Bunny account and go to Settings > Company.
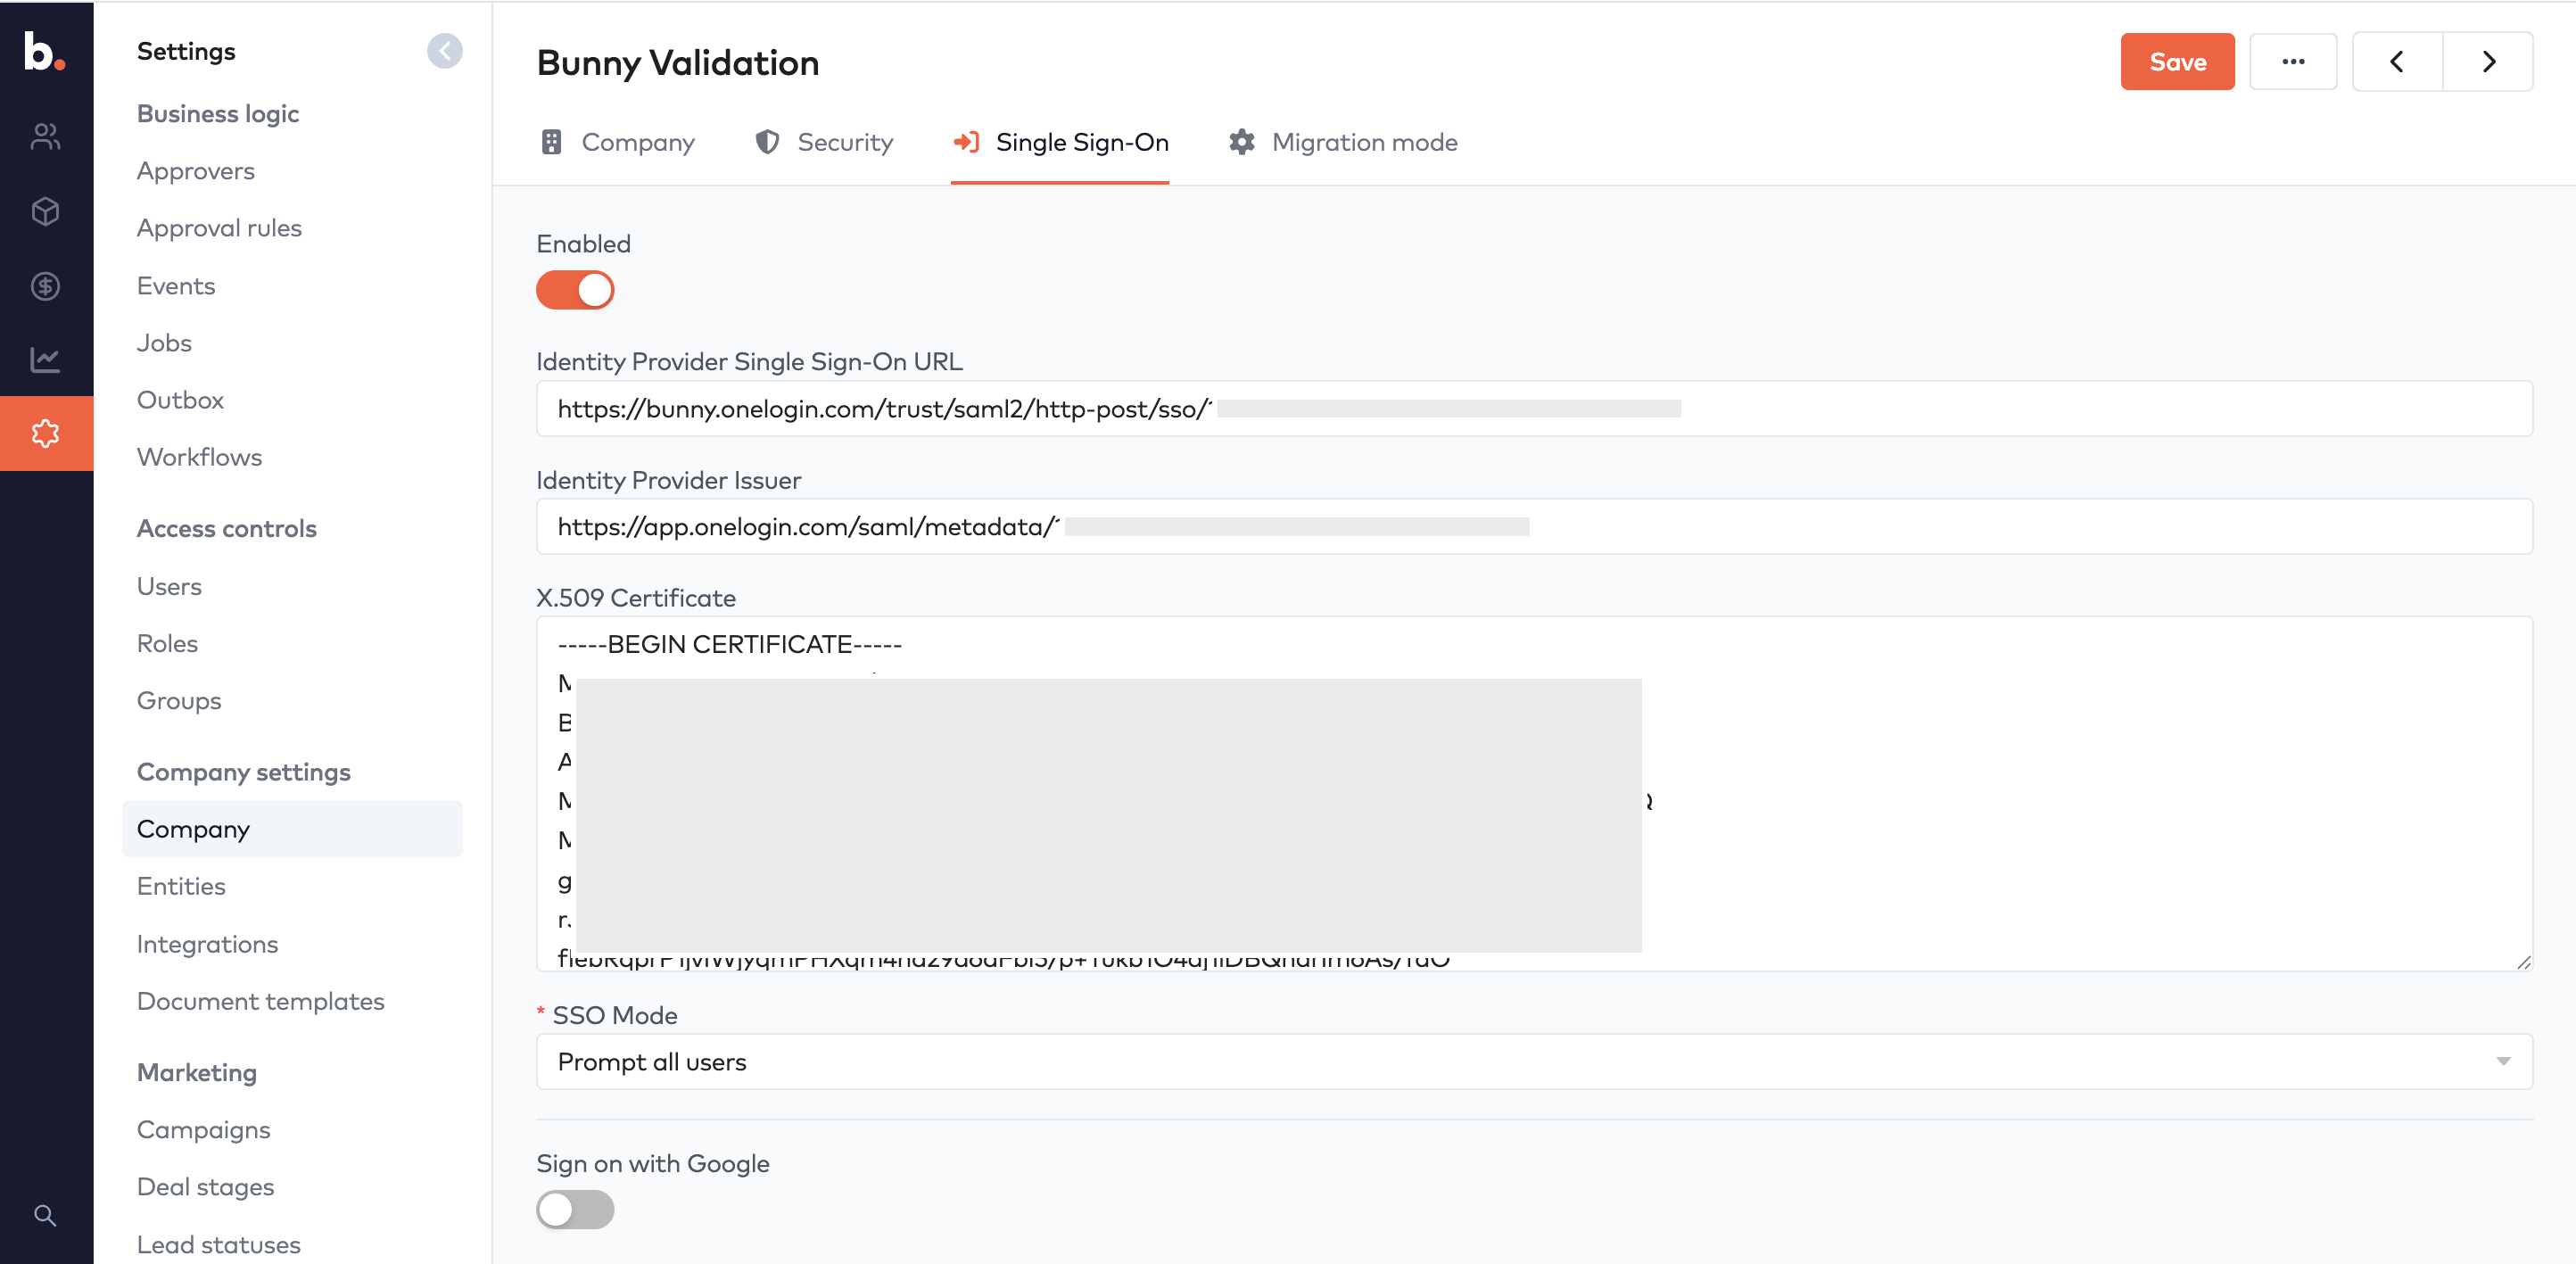
Bunny SSO settings
- Now select the Single Sign-On tab
- Then, toggle the Enabled switch to the on position
- And copy/paste the following fields over from your identity provider
Switch to the SSO tab on the application you created in step 1.
| Onelogin field | Bunny field |
|---|---|
| SAML 2.0 Endpoint (HTTP) | Identity Provider Single Sign-On URL |
| Issuer URL | Identity Provider Issuer |
| <p>On the Onelogin application click under X.509 Certificate click View Details. Then copy the certificate starting with “—–BEGIN CERTIFICATE—–”</p> |
X.509 Certificate |
From the SAML setup instructions copy the following to Bunny
| Okta field | Bunny field |
|---|---|
| Identity Provider Single Sign-On URL | Identity Provider Single Sign-On URL |
| Identity Provider Issuer | Identity Provider Issuer |
| X.509 Certificate | X.509 Certificate |
Step 3 - Test the single sign-onLink to Step 3 - Test the single sign-on section
As as security best practive there is no backdoor for the Bunny account owner to change SSO settings which means if you have not got the configuration right you will not be able to login.
We recommend that you test the SSO login in a different browser so that you can keep your existing Bunny session alive in case any changes need to be made.